Know what’s dangerous on your servers, and how to fix it.
Outdated packages, exposed containers, weak configs. Staunch finds them and tells you what to do.
Check your inbox.
Click the link in the email we just sent to your address to confirm your spot.
- web-fra-012 criticalUbuntu 26.04
- api-fra-012 highDebian 13
- db-fra-01No issuesDebian 13
web-fra-01
- Status
- Online
- OS
- Ubuntu 26.04
- IP
- 203.0.113.24
- Uptime
- 41 days
Security score 58 out of 100
AI summary
Redis and the Docker API are open to anyone on the Internet, so close them first. Then update the kernel.
- 1CriticalRedis is reachable from the Internet
Port 6379 is published on all interfaces. Anyone can read or wipe your cache.
docker-compose.ymlThe exact fix, ready to copy.cache:ports: ["6379:6379"]ports: ["127.0.0.1:6379:6379"] - 2CriticalDocker API is exposed on port 2375
- 3Ranked by exploitability, not alphabetically.High12 security updates pending and 1 actively exploited
- 4HighSSH accepts password logins
Security score
Security score 58 out of 100
Needs attention
Last 14 days−13 since Monday
Health
- CPU23%2 vCPU, load 0.42
- Memory61%2.3 of 3.8 GB
- Disk88%41 of 47 GBFull in about 9 days
From install to answers in minutes.
Step 1: Install the agent
One command, one small binary. No inbound ports to open.
Step 2: Staunch checks everything
Packages, containers, system configuration and server health, around the clock.
Step 3: Fix what matters first
Open your dashboard and get a prioritized list, with the reason, the risk and the exact fix for every issue.
Installing will look like this:curl -fsSL https://get.staunch.sh | sh
What Staunch checks
Packages
Containers
Configuration
Monitoring
Alerts by email, Slack, Discord, Telegram or webhook. One alert per incident, only when it needs you.
AI analysis
Detection comes from strict, documented rules. The AI explains and prioritizes.
Built to run on production servers.
Read-only agent
Staunch never changes anything on your server. It looks, and it reports.
Outbound only
The agent connects out over HTTPS. Nothing to open, nothing listening.
Hosted in Europe
Your data is stored and processed in the European Union.
Only what’s needed
The agent collects what the checks need. Never your files, databases or app data.
Simple pricing. Start free.
Free
Try Staunch on one server.
Join the waitlist$0€0
No card needed
- 1 server
- All detection modules
- Daily security scan
- Downtime and email alerts
- 7-day history
- Weekly AI summary
Pro
For developers running a few servers.
Join the waitlist$19€19/month
Instead of $19€19$15.83€15.83/monthBilled monthly$190€190 billed yearly
- 3 servers included
- $5€5 per extra server
- Hourly security scan
- Slack, Discord, Telegram and webhook alerts
- 30-day history
- AI prioritization and full weekly report
Team
For small teams sharing infrastructure.
Join the waitlist$49€49/month
Instead of $49€49$40.83€40.83/monthBilled monthly$490€490 billed yearly
- Everything in Pro
- 10 servers included
- $4€4 per extra server
- Up to 5 members, with roles
- 90-day history
Founding members
Join the waitlist before launch and keep 20% off any paid plan for as long as you stay. Monthly or yearly, on top of the 2 free months.
Prices exclude taxes.Prices exclude VAT.
Frequently asked questions
Do I need to know security to use Staunch?
No, that’s the point. Every issue comes with what’s wrong in plain words, why it matters, and the exact fix to copy. No security advisories to decode, no forums to dig through.
I already have a firewall. Isn’t that enough?
Not always. Docker opens container ports through its own rules, so a port your firewall blocks can still be reachable from the Internet. Staunch checks what’s actually exposed, not just what your firewall says.
How is it different from a vulnerability scanner?
A scanner hands you hundreds of CVEs and leaves the rest to you. Staunch looks at the whole server, from packages to containers to configuration, ranks what attackers can actually reach, and tells you the few things to fix first.
What data leaves my server?
System metrics, the list of installed packages, container settings and the results of configuration checks. Never your files, databases or application data. Everything is stored and processed in the European Union, and the full list will be public before launch.
Can Staunch change anything on my server?
No. The agent is read-only and only connects out, so there’s no new port to open. Staunch tells you what to fix and how, and every change stays in your hands.
Does the agent need root?
Some checks need elevated read access, like reading the SSH configuration or listing containers. Every permission will be documented, along with what it’s used for.
Which systems are supported?
Ubuntu and Debian at launch, with or without Docker. RHEL, Rocky, Alma and Alpine are next.
Is there a free plan?
Yes. The Free plan covers one server with every detection module and a daily scan. No card needed.
When does Staunch launch?
Early access opens in 2027. People on the waitlist get in first, and founding members keep 20% off any paid plan for as long as they stay.
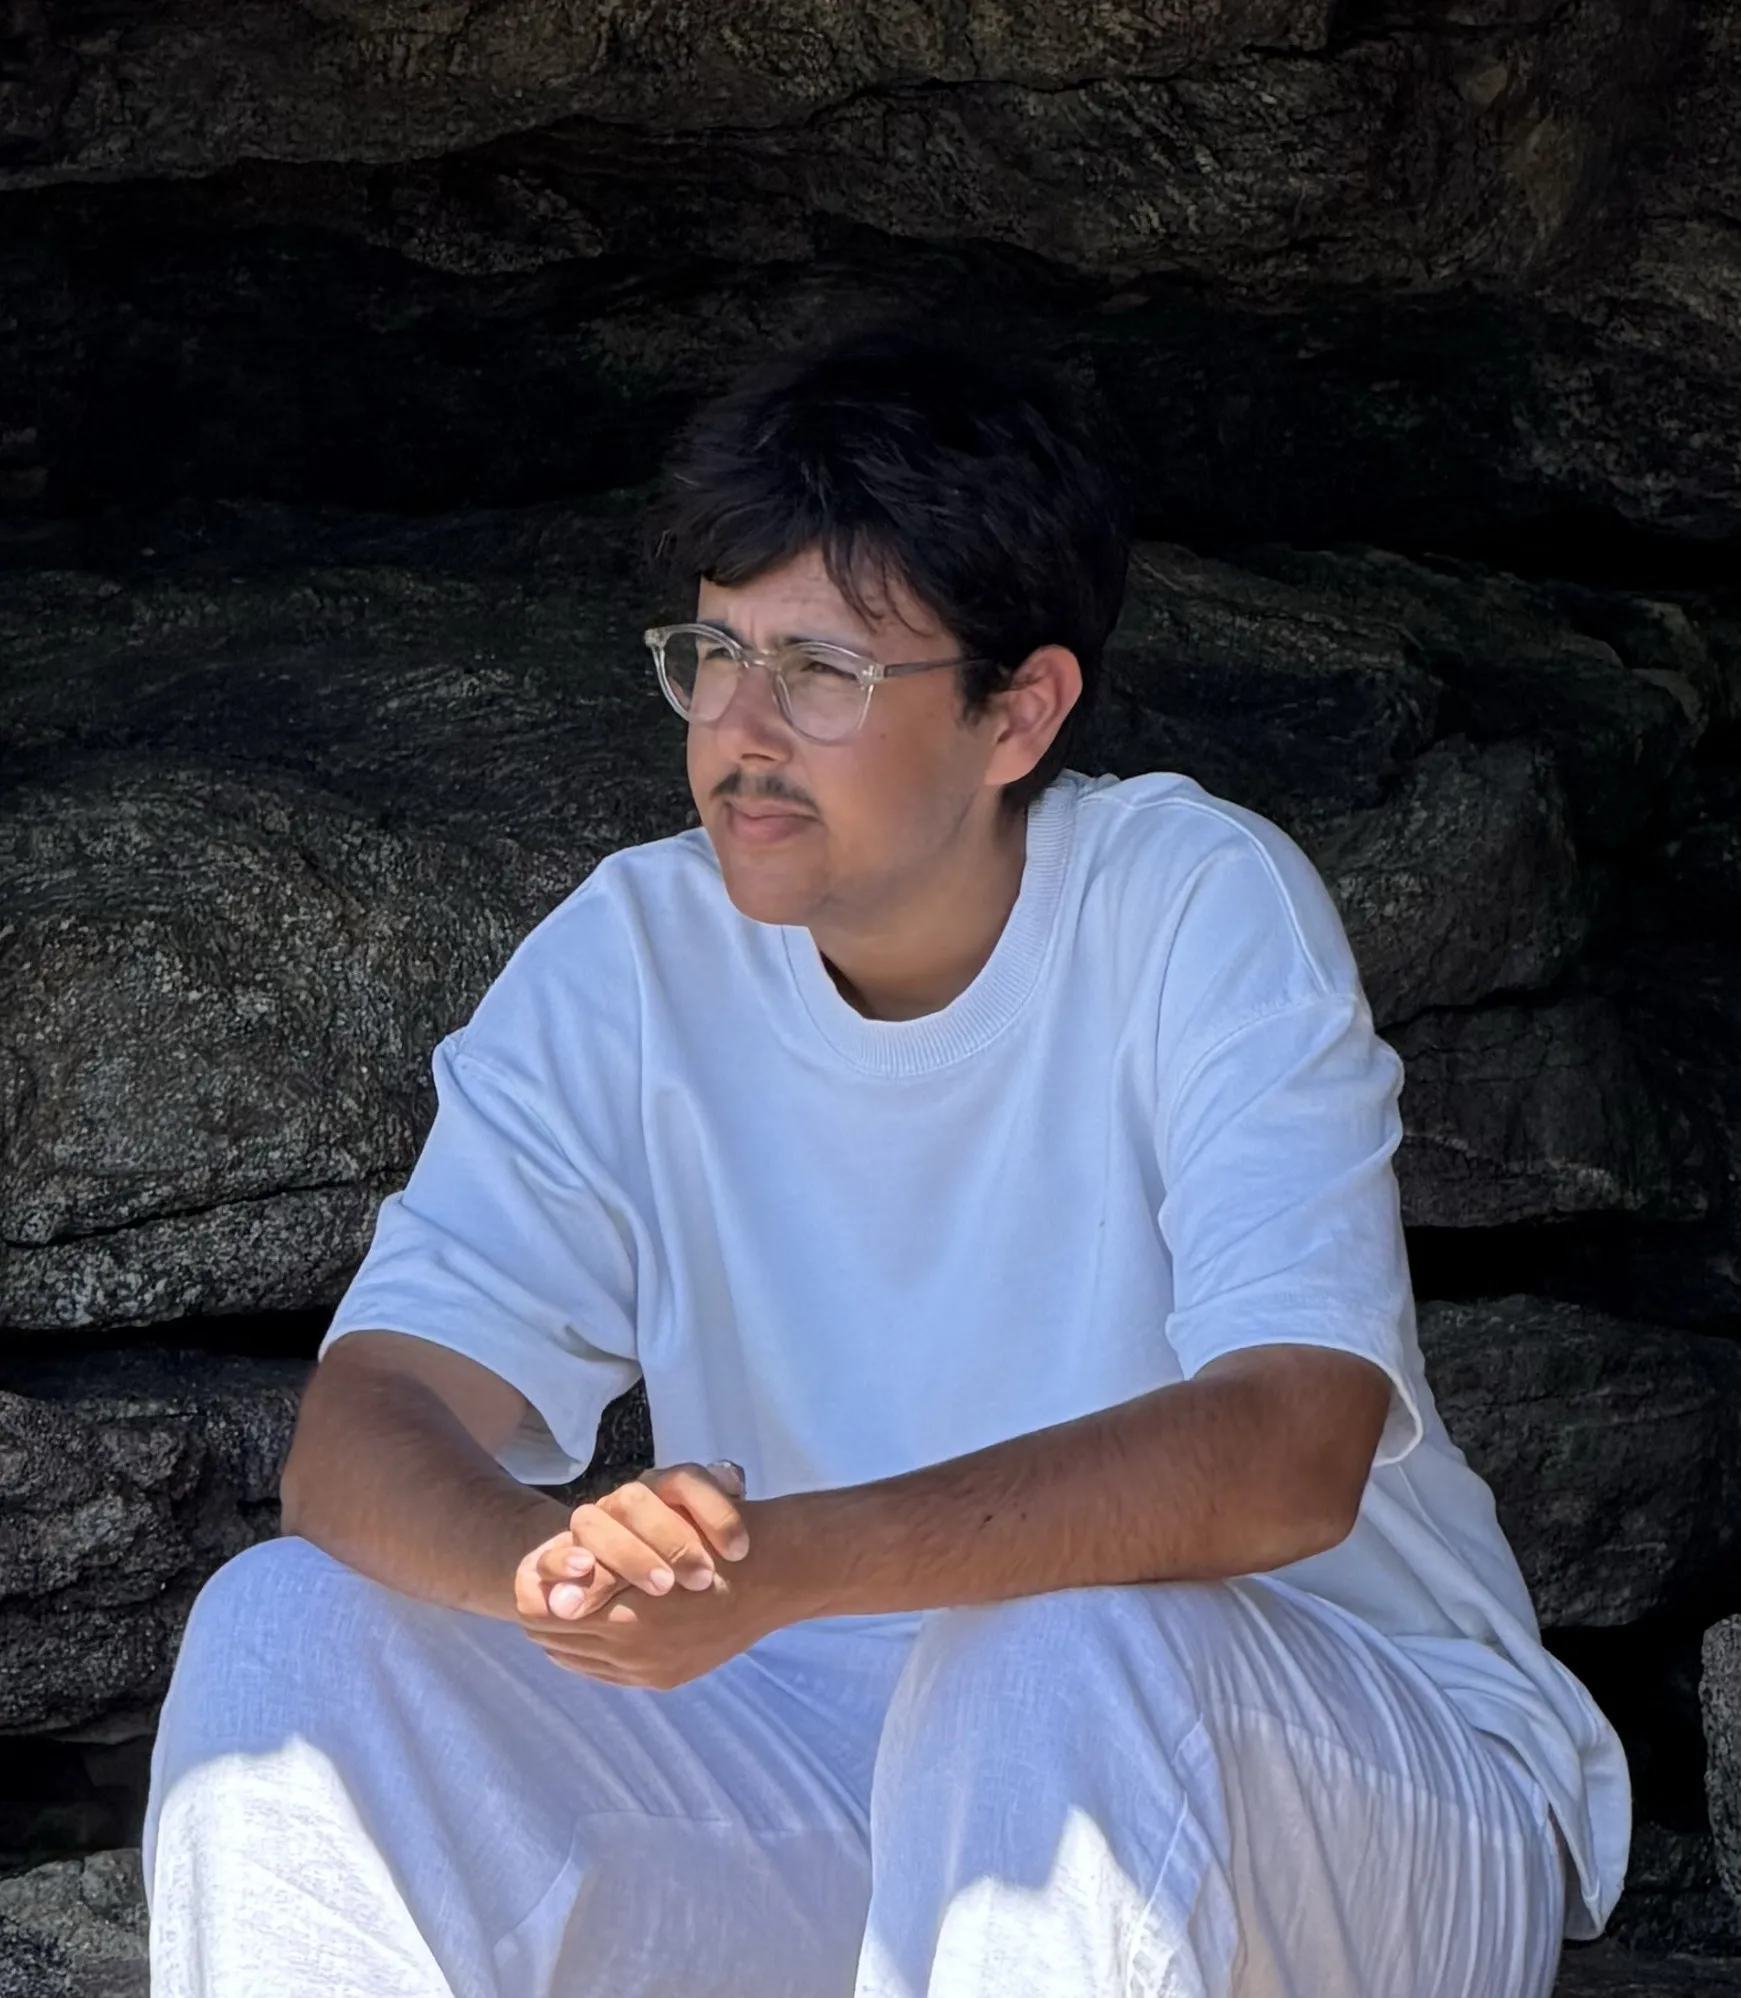
Who’s building Staunch
I deal with servers every day at work, and I keep seeing the same thing: servers that go live in minutes, then never get checked again. So I’m building the tool I wanted.
Mael DuretDeveloper and DevOps engineer, France
Read why I’m building StaunchStop guessing what’s exposed.
Join the waitlist and be first in when early access opens.
Check your inbox.
Click the link in the email we just sent to your address to confirm your spot.